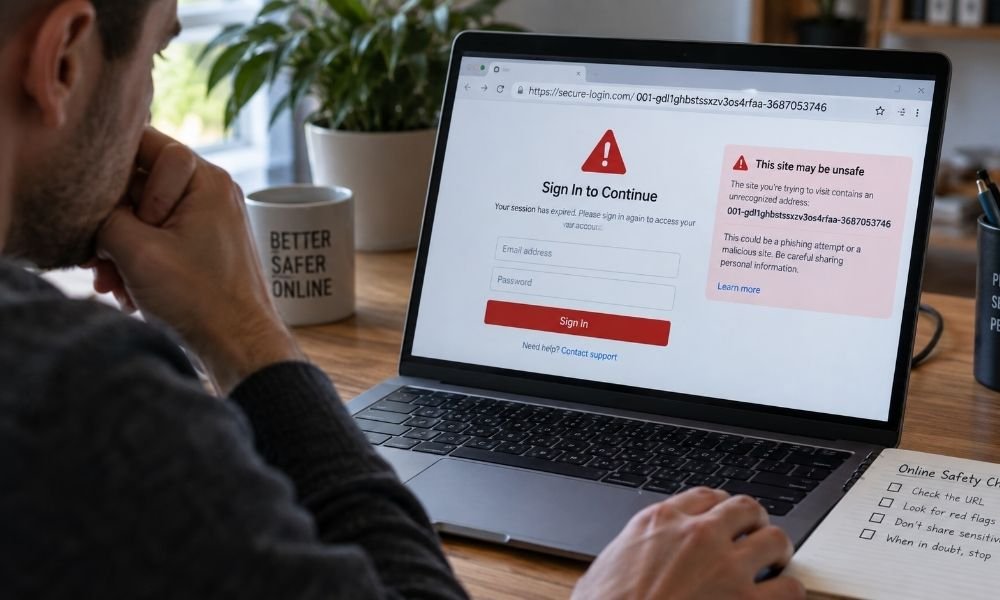
A strange code can make anyone stop and think. You may see 001-gdl1ghbstssxzv3os4rfaa-3687053746 in a link, email, browser history, or pop-up. It may look scary because it is long and hard to read. It may also look like something hidden. But the code alone does not prove danger. Many safe websites use long codes every day. The real question is simple. Where did you see it? A trusted website is very different from a strange email or fake login page. This guide explains what 001-gdl1ghbstssxzv3os4rfaa-3687053746 may mean, when it may be safe, and when you should be careful.
What Is 001-gdl1ghbstssxzv3os4rfaa-3687053746?
001-gdl1ghbstssxzv3os4rfaa-3687053746 looks like a machine-made ID. It is not a normal word. It is not a clear brand name. Public pages that discuss this exact string often describe it as a possible unique identifier, which means a code used by a system to point to one item, page, file, session, or record. A code like this can help software keep things in the right place. Think of it like a ticket number. The ticket number may look odd, but it helps a system find one item without mixing it with another item.
The Code Alone Does Not Mean It Is Unsafe
It is important not to panic when you see 001-gdl1ghbstssxzv3os4rfaa-3687053746. Text by itself is not a virus. A string of letters and numbers cannot harm your device just because you look at it. The risk comes from what is around the code. Is it inside a strange link? Does the page ask for your password? Does it push you to download a file? Does it say your account will close today? These things matter more than the code itself. A safe site can use an odd code. A scam site can also use a normal-looking link. Context is the main clue.
Why Long Codes Appear in Links
Websites often use long codes to remember what a visitor is doing. A shopping site may use a code to open the right order page. A support site may use a code to show the right ticket. A file-sharing page may use a code to find the right file. A login system may use a code to manage a session. So 001-gdl1ghbstssxzv3os4rfaa-3687053746 could appear for a normal technical reason. Still, OWASP warns that session IDs placed in URLs may be exposed through browser history, bookmarks, logs, referrer headers, and search engines. That is why sensitive codes should be handled with care.
When 001-gdl1ghbstssxzv3os4rfaa-3687053746 May Be Safe
001-gdl1ghbstssxzv3os4rfaa-3687053746 may be safe when it appears in a place you trust. For example, you may see it after opening a real support page, receipt page, order page, or account setting page. It may also appear after clicking a link from a company you already know and use. Safe signs are usually clear. The domain name is spelled right. The page uses HTTPS. Your browser does not show a warning. The page does not ask for strange details. The page looks like the real site you expected. Even then, you should not share private links with other people if the link contains a personal session or account code.
When 001-gdl1ghbstssxzv3os4rfaa-3687053746 May Be Unsafe
001-gdl1ghbstssxzv3os4rfaa-3687053746 may be unsafe when it appears inside a strange or urgent message. Be careful if the message says you must act now. Be careful if it says your bank account, social account, or email will close. Be careful if the link sends you to a page that asks for your password, card number, recovery code, or one-time code. A long code can be used to track who clicked a link. It can also be used inside a redirect. A redirect means one link sends you to another page. Some redirects are safe. But unknown redirects can hide the real final page.
Common Warning Signs
You do not need to be a tech expert to notice danger. Look for simple signs before you click or type anything.
-
The sender is unknown.
-
The message has fear or pressure.
-
The website name is misspelled.
-
The page asks for a password too quickly.
-
The link opens many pages before landing.
-
The page asks you to download a file.
-
The page says your device is infected.
-
The offer sounds too good to be true.
If 001-gdl1ghbstssxzv3os4rfaa-3687053746 appears with these signs, treat the page with care. Close it and go to the real website by typing the address yourself.
Why Scammers Use Random-Looking Codes
Scammers may use random-looking codes because codes help them control a campaign. They may use a code to know which email got a click. They may use a code to send different users to different pages. They may also use codes to make a link look technical and less easy to understand. This does not mean 001-gdl1ghbstssxzv3os4rfaa-3687053746 is always part of a scam. It means the same kind of pattern can be used in both safe and unsafe ways. A tool is not the problem by itself. The problem is how the tool is used.
Check the Domain Before the Code
The domain name is more important than the long code. The domain is the main website name, like the real name of a bank, store, school, or app. If you see 001-gdl1ghbstssxzv3os4rfaa-3687053746 in a link, look at the domain first. A scammer may place a long code after a fake domain. Many users focus on the last part of a link and miss the site name. This is risky. A safe code on a fake domain is not safe. A strange code on a real domain may be normal. Always read the website name slowly.
What To Do Before You Click
A few checks can save you from a bad page. These checks are simple, and they work for many kinds of strange links. They are also useful for children, older users, and busy workers who click messages fast. The goal is not to fear every link. The goal is to slow down when the page does not feel right.
Before clicking a link with 001-gdl1ghbstssxzv3os4rfaa-3687053746, pause for a few seconds. If you are on a computer, place your mouse over the link and look at the full address. Do not click if the domain looks wrong. If you are on a phone, press and hold the link to preview it when possible. Do not trust a message just because it has a logo. Logos can be copied. Do not enter your login details after clicking a link from an unknown message. Open the real website in a new tab instead. This small habit can stop many common scams.
What To Do If You Already Clicked
Do not panic if you clicked a link with 001-gdl1ghbstssxzv3os4rfaa-3687053746. Clicking alone does not always mean your device is infected. First, think about what happened after the click. Did you only open a page and close it? That is often less serious. Did you enter a password? Did you download a file? Did you share bank details? That is more serious. If you entered a password, change it from the real website. Turn on two-factor login. Log out of other sessions if the account gives that option. Check recent activity. If you downloaded a file, delete it and run a scan.
Privacy Risk: Why Session IDs Matter
Some long codes work like session IDs. A session is the short time when a website remembers your visit. For example, a site may remember that you are logged in, or that you placed items in a cart. OWASP explains that applications use session identifiers to track authenticated state and user progress during a session. If a session ID is exposed, another person may learn things they should not see. Good websites try to protect session data. They often keep sensitive tokens out of the visible URL. Still, users should be careful with any link that includes 001-gdl1ghbstssxzv3os4rfaa-3687053746 if the page is connected to login, money, private files, or account settings.
Simple Safety Rule
Here is the best rule. Do not judge 001-gdl1ghbstssxzv3os4rfaa-3687053746 by the code alone. Judge the place where you found it. A strange code in a trusted receipt page may be normal. The same kind of code in a fake bank email may be dangerous. Look at the sender, domain, message tone, page design, and request. A safe page will not rush you. A safe page will not ask for secret codes without reason. A safe page will not scare you into fast action. Slow checking is better than fast clicking.
A Helpful Example
Imagine you receive a message that says your account has a problem. The message includes a link with a long code at the end. The sender name looks close to a real company, but one letter in the domain is wrong. The page asks for your password and a one-time code. This is a warning sign. Now imagine you are already signed in to a real shopping site. You open your order page, and a long code appears after the address. The page shows your order and does not ask for secret details. That may be normal. The difference is not only the code. The difference is the source, the page behavior, and the request.
Final Thoughts
001-gdl1ghbstssxzv3os4rfaa-3687053746 is not automatically unsafe. It looks like a machine-made identifier. Many online systems use codes like this for normal reasons. But any strange code can become a warning sign when it appears in a risky place. Be careful with unknown emails, redirects, login pages, pop-ups, and downloads. Check the domain before you trust the link. Do not share passwords, card details, or one-time codes on pages you did not expect to open. The safest answer is simple. 001-gdl1ghbstssxzv3os4rfaa-3687053746 may be harmless in the right place, but it should be treated with care in the wrong place.